
note to self

so I have been using theme twenty eleven for.. heh.. 10 years :)
turns out it is not compatible with modern browsers/OSs using dynamic light/dark theme. in particular the “code” block that I frequetly use causes certain browsers to display dark text on dark background.. and that changes depending on the time of the day depending on the user OS and/or browser.. which is too much for me too look into.
so I am changing the site back from dark/orange to light as the OS / the browser apparently wants to decide to invert the colors – time to find a new theme, I guess. It’s been fun, thank you <3

file-level encryption using ecryptfs seems unnaturally easy… too easy some would say.
sure, full-disk should be better, I just want to have a way to hide stuff from prying eyes.
basically you just point it to a folder and that’s it. suspiciously easy.
you need: ecryptfs-utils (via your friendly package manager or compile it yourself…)
then just go and mount the directory using -t ecryptfs
sudo mount -t ecryptfs ~/cat_pictures/ ~/cat_pictures/this will encrypt the folder “cat_pictures” in your home folder. Be sure it exists but is empty when you run this for the first time (otherwise already existing data will not be encrypted)
it does ask some questions: remember the “passphrase” is the key to decrypt the data.
Passphrase:
Select cipher:
 1) aes: blocksize = 16; min keysize = 16; max keysize = 32
 2) blowfish: blocksize = 8; min keysize = 16; max keysize = 56
 3) des3_ede: blocksize = 8; min keysize = 24; max keysize = 24
 4) twofish: blocksize = 16; min keysize = 16; max keysize = 32
 5) cast6: blocksize = 16; min keysize = 16; max keysize = 32
 6) cast5: blocksize = 8; min keysize = 5; max keysize = 16
Selection [aes]:
Select key bytes:
 1) 16
 2) 32
 3) 24
Selection [16]:
Enable plaintext passthrough (y/n) [n]:
Enable filename encryption (y/n) [n]:
Attempting to mount with the following options:
  ecryptfs_unlink_sigs
  ecryptfs_key_bytes=16
  ecryptfs_cipher=aes
  ecryptfs_sig=XXXXXXXXXXXXXXXXXX
WARNING: Based on the contents of [/root/.ecryptfs/sig-cache.txt],
it looks like you have never mounted with this key
before. This could mean that you have typed your
passphrase wrong.

Would you like to proceed with the mount (yes/no)? : yes
Would you like to append sig [XXXXXXXXXXXXXx] to
[/root/.ecryptfs/sig-cache.txt]
in order to avoid this warning in the future (yes/no)? : yes
Successfully appended new sig to user sig cache file
Mounted eCryptfs
that’s it – the folder is now mounted. Go and fill it with data.
unmount with
sudo umount ~/cat_pictures/if you want to mount it again
sudo mount -t ecryptfs ~/cat_pictures/ ~/cat_pictures/mind you, all options need to be answered in the same way… so you could make this easier by creating a script.. or using a wrapper.. but then, what’s the point of encryption if you store the key in a file???
Edit: turns out you can: edit/create /root/.ecyptfsrc
ecryptfs_enable_filename_crypto=y
ecryptfs_passthrough=n
ecryptfs_unlink_sigs
ecryptfs_fnek_sig=xxxxxxxxxxxxxxxxxxxx
ecryptfs_key_bytes=16
ecryptfs_cipher=aes
ecryptfs_sig=xxxxxxxxxxxxxxxxx
sources:
I was this years old when I discovered that those two are an incredible combination… and I will probably regret this discovery ;)

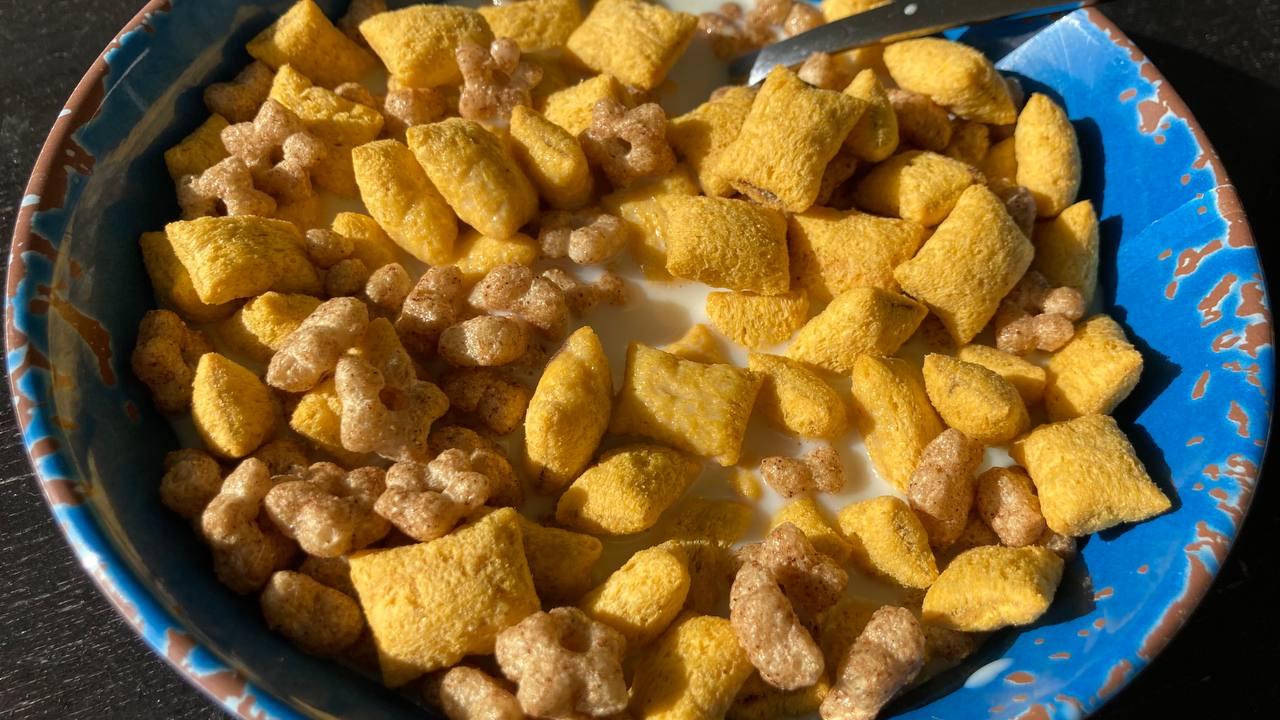
so.. no pancakes today, I guess


(found on the internet)
So Alfa Romeo race drivers put a cloverleaf on their cars for good luck. I think this needed a 21st century upgrade.
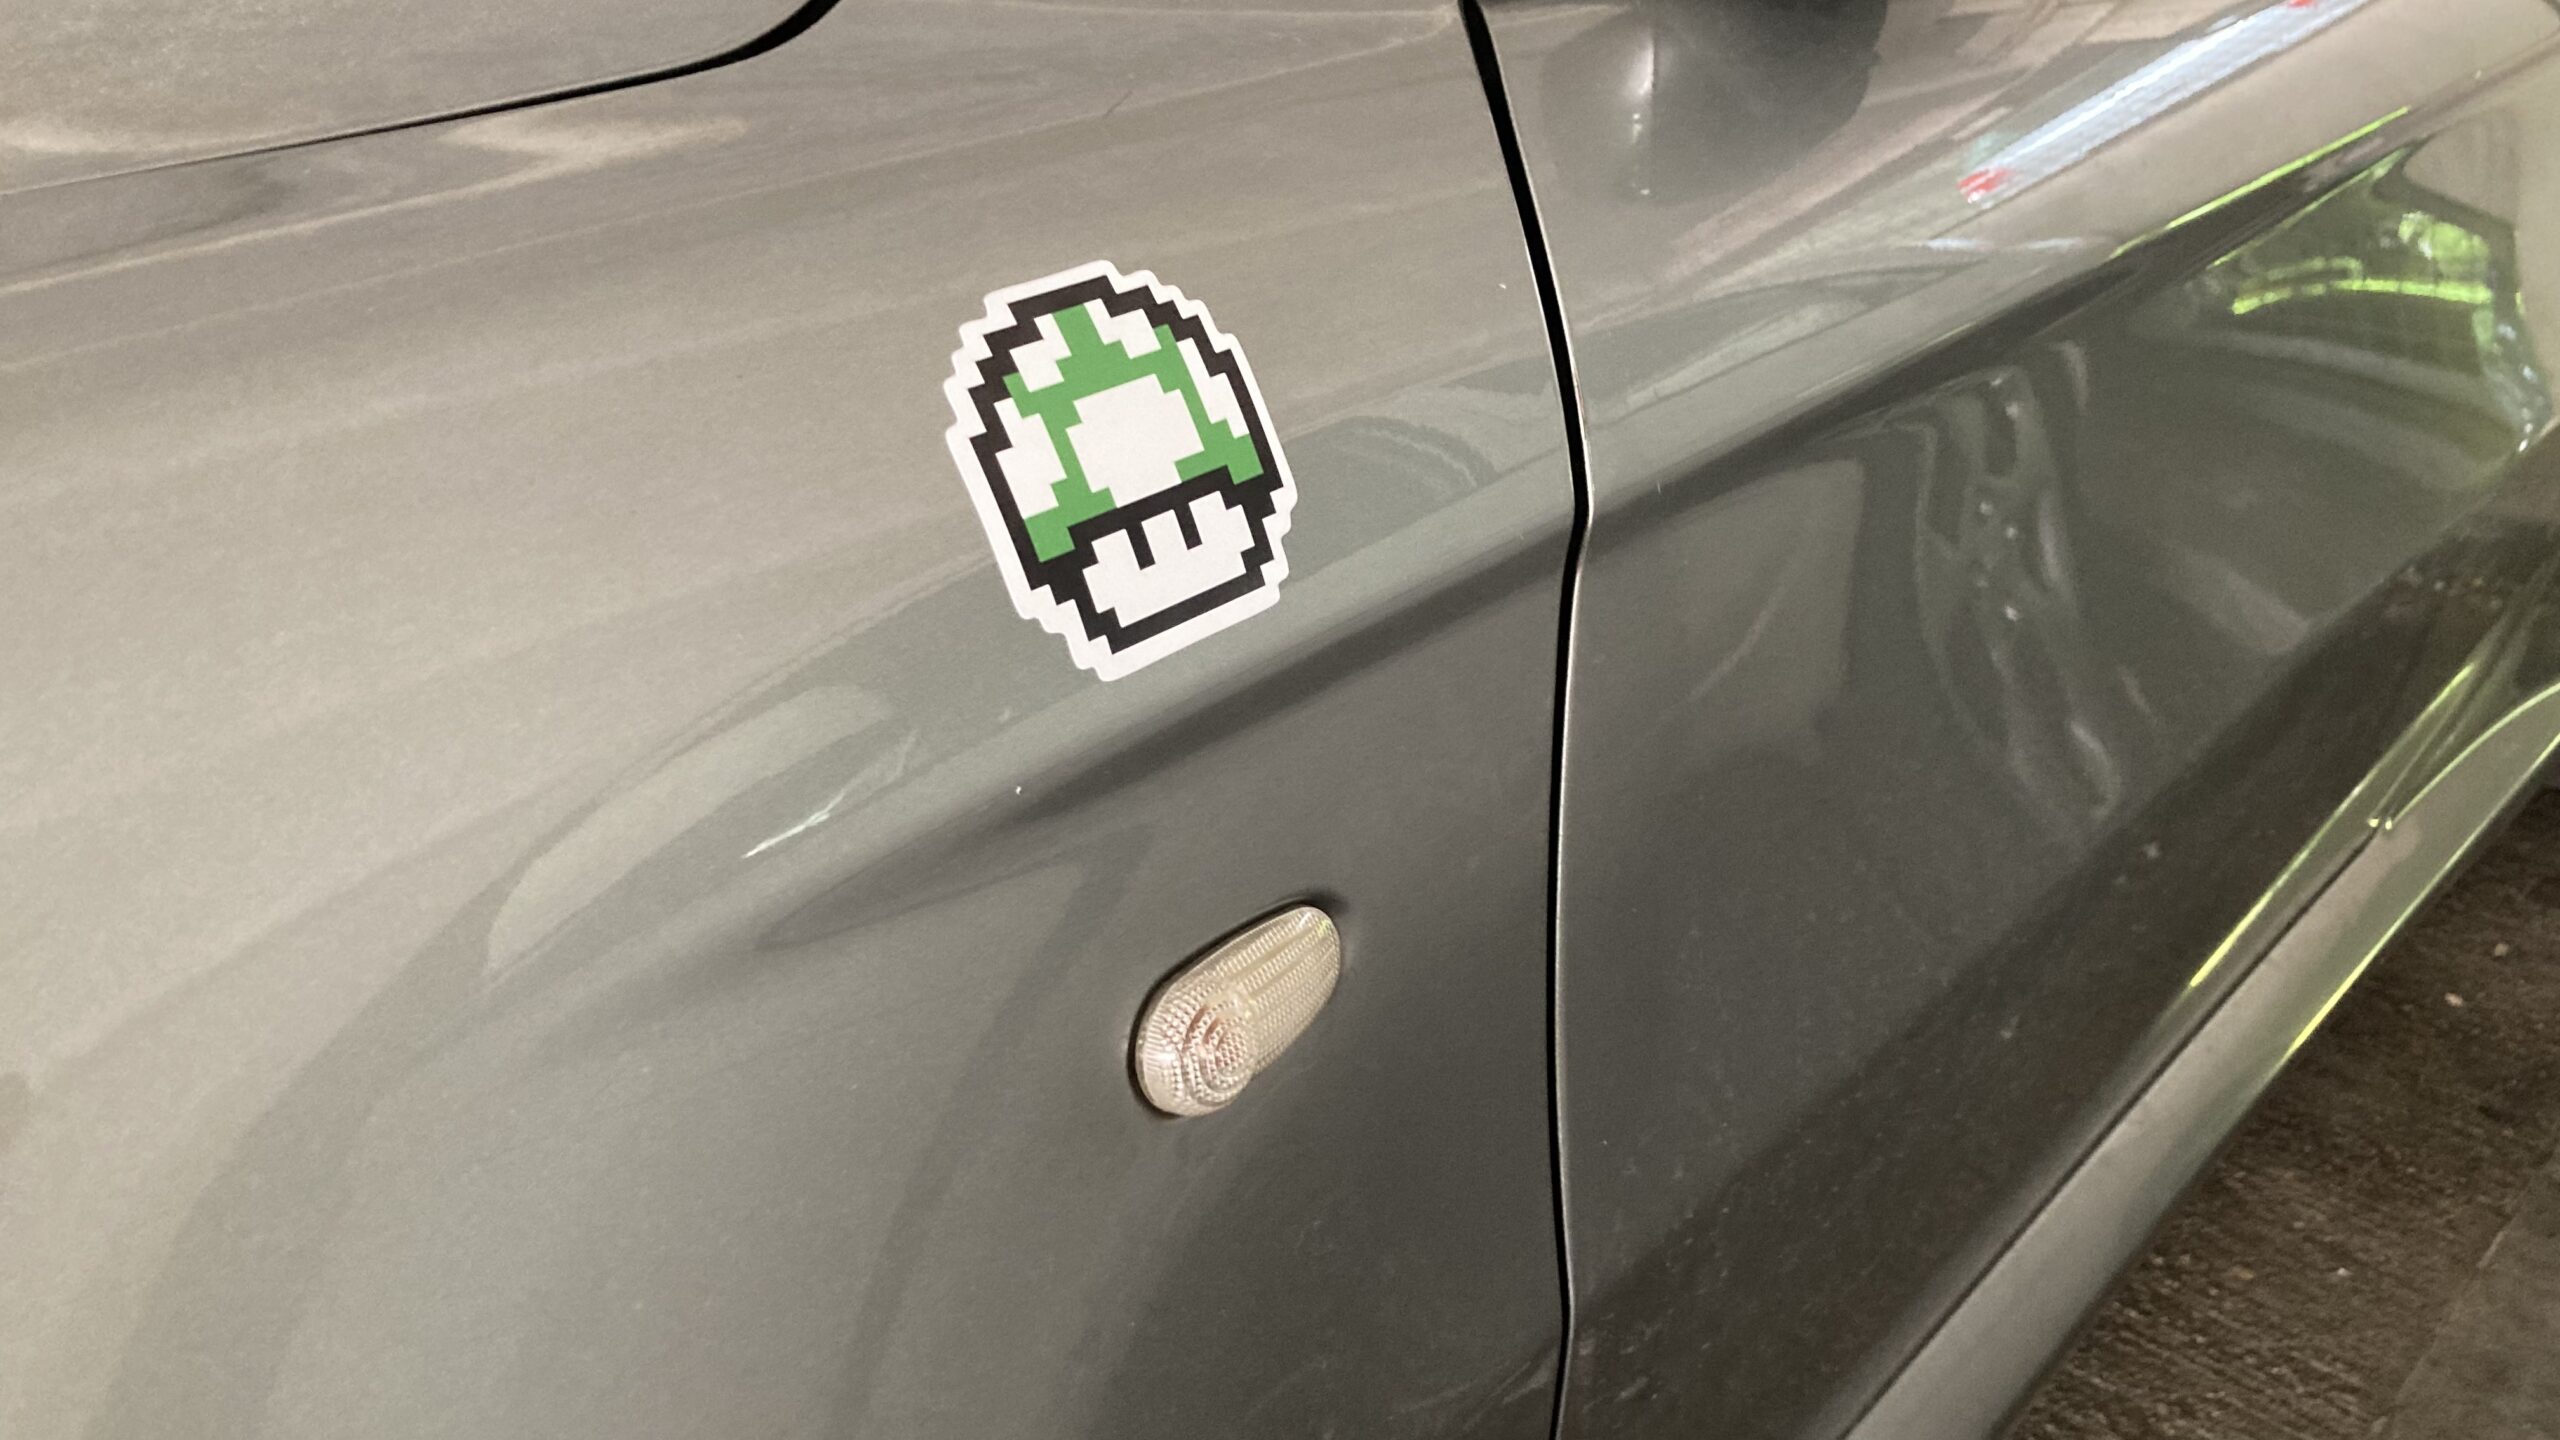
After 10 years of lease cars I am thrilled to actually OWN a car where I can slap stickers on or drill holes into it because… its MINE and no one can stop me ^ ^ (besides maybe the RDW)
I got my nands on an old Fujitsu MX microserver and decided to give proxmox a spin. Some notes:
4 x HDD from old laptops perform well without sync… use with caution and have backups.
root@proxmox:~# pveperf /XXX-raid/
CPU BOGOMIPS: 55998.56
REGEX/SECOND: 4163519
HD SIZE: 899.00 GB (XXX-raid)
FSYNCS/SECOND: 147.26
DNS EXT: 38.15 ms
DNS INT: 20.83 ms (home)

root@proxmox:~# zfs set sync=disabled XXX-raid

root@proxmox:
~# pveperf /XXX-raid/
CPU BOGOMIPS: 55998.56
REGEX/SECOND: 4173357
HD SIZE: 899.00 GB (XXX-raid)
FSYNCS/SECOND: 3986.33
DNS EXT: 39.74 ms
DNS INT: 21.05 ms (home
adding two SSDs in front of two slow harddisks have the same effect. (add them as ZIL for IOPS, add them as LOG to mitigate write delays / latency)
benchmark with pveperf first, then with fio
Mind your ashift. 12 == 4k, 9 == 512b
fastest way to zap disks to use them:gdisk /dev/sda
'x' for extra commands
'z' for zap
some days are just more sucky than others.. usually right after those awesome days.